The Wiert Corner – irregular stream of stuff

Jeroen W. Pluimers on .NET, C#, Delphi, databases, and personal interests

  • My badges

  • Twitter Updates

  • My Flickr Stream

  • Pages

  • All categories

  • Email Subscription

    Enter your email address to subscribe to this blog and receive notifications of new posts by email.

    Join 717 other subscribers

Archive for the ‘Infosec (Information Security)’ Category

Cyber Gangsta’s Paradise | Prof. Merli ft. MC BlackHat [Parody Music Video] – YouTube

Posted by jpluimers on 2025/05/16

Cyber Gangsta’s Paradise | Prof. Merli ft. MC BlackHat [Parody Music Video] – YouTube [Wayback/Archive]

Cyber Gangsta’s Paradise; professor Merli featuring MC Blackhat

#ParodyMusicVideo #cybergangster #paradise #reimtsich

Via @christopherkunz@chaos.social [Wayback/Archive]

The video is on the walled garden called Instagram as well, but since I intentionally don’t have an account there accessing is hard. Anyway, it is at: [WaybackSave/Archive] Instagram: „Cyber Gangsta’s Paradise“ feiert Premiere 🎶🎬.

In the past, picuki was an alternative. Now it fails for instagram content.  [Wayback/Archive] Instagram Reels Download with Reels Downloader got me to [Wayback/Archive] cdninstagram, which in the end worked.

Transcript (via Google, typos all mine), song-text (from video description), and of course the credits:

Read the rest of this entry »

Posted in Blue team, Cyber, Infosec (Information Security), Power User, Red team, Security | Tagged: , , , | Leave a Comment »

Reminder to self: re-check the Dotpe API Security Breach — bool.dev

Posted by jpluimers on 2025/03/04

Still public merchant information

Still public merchant information

It looks like some store and merchang APIs were not protected back when [Wayback/Archive] Dotpe API Security Breach — bool.dev was published.

Reminder to self: check their status now as I can’t believe their “human error” got fixed properly.

History (reverse chronological order):

  1. [Wayback/Archive] How DotPe’s ‘Human Error’ Exposed Confidential Customer API Data
  2. [Wayback/Archive] Deedy on X: “Today, Google-backed DotPe locked down their APIs by rate-limiting by IP on /external/merchant and blocking others. They sent a legal notice to the author before fixing it and haven’t publicly acknowledged the issue at all. Companies must be held accountable for poor security.…”

    [Wayback/Archive] Tweet JSON: [Wayback/Archive] GYSlTthakAEoojp.png:orig (2346×1838)

  3. Now protected private API

    Now protected private API

    [Wayback/Archive] Deedy on X: “6 hours later, the API is still very much public! …”

    [Wayback/Archive] Tweet JSON: [Wayback/Archive] GYK38dXbkAEEEs_.jpg:orig (1358×1798)

Read the rest of this entry »

Posted in Communications Development, Development, HTTP, Infosec (Information Security), Internet protocol suite, REST, Software Development, TCP, Web Development | Leave a Comment »

What’s inside the QR code menu at this cafe? – by peabee

Posted by jpluimers on 2024/09/27

This is why I do not trust ordering via QR-code: you never know how good (or usually bad, often even non-existent) their security is.

[Wayback/Archive] What’s inside the QR code menu at this cafe? – by peabee is a really bad example about Google backed DotPe: they have zero-auth and by now have rated limited API access by IP address.

…

I went to a cafe near my home. I sat down and scanned the QR code on the table. It took me to a website displaying the cafe’s menu. It asked me for my name and Whatsapp mobile number. I entered the details and placed the order.

In 5 mins my order arrived at the table. There was no OTP verification, and no one came to confirm the order. Is this what the peak ordering experience looks like?

It was a slow workday, and I thought I might as well open this QR code website on my laptop and have a quick look under the hood. Maybe I should’ve just made my own coffee and stayed home because I didn’t realize I was opening a can of worms.

…

This kind of zero-auth is not infrequent: the Panels API and CDN were wide-open too: [Wayback/Archive] https://storage.googleapis.com/panels-api/data/20240916/media-1a-i-p~s

Read the rest of this entry »

Posted in Authentication, Development, Infosec (Information Security), LifeHacker, Phishing, Power User, Security, Software Development | Tagged: | Leave a Comment »

XZ 5.6.x are backdoored and present in many systems: downgrade to 5.4.x or earlier now; consider libarchive compromised until proven otherwise

Posted by jpluimers on 2024/03/30

Edit 20240331: because of

https://mastodon.social/@kobold@social.troll.academy/112183756981119562

Debian is working on reverting back to even earlier than 5.4.x

[Wayback/Archive] #1068024 – revert to version that does not contain changes by bad actor – Debian Bug report logs

> I'd suggest reverting to 5.3.1. Bearing in mind that there were security
> fixes after that point for ZDI-CAN-16587 that would need to be reapplied.

Note that reverted to such an old version will break packages that use
new symbols introduced since then. From a quick look, this is at least:
- dpkg
- erofs-utils
- kmod

Having dpkg in that list means that such downgrade has to be planned
carefully.


Original post:

Everything I know about the XZ backdoor

Note that because of the Wayback Machine limit of 5 archivals per URL per day, the archived versions are rapidly getting out-of-date.

It is way worse:

[Wayback/Archive] Thread by @_ruby on Thread Reader App – Thread Reader App

@_ruby: The setup behind the CVE-2024-3094 supply-chain attack is fascinating. I originally wanted to finish and share a tool to audit other OSS projects for anomalous contributor behavior, but I feel what I found tr……

How it was found:

Analogy on how it was found:

Via:

Related:

If you are running homebrew on a Mac, then update too:

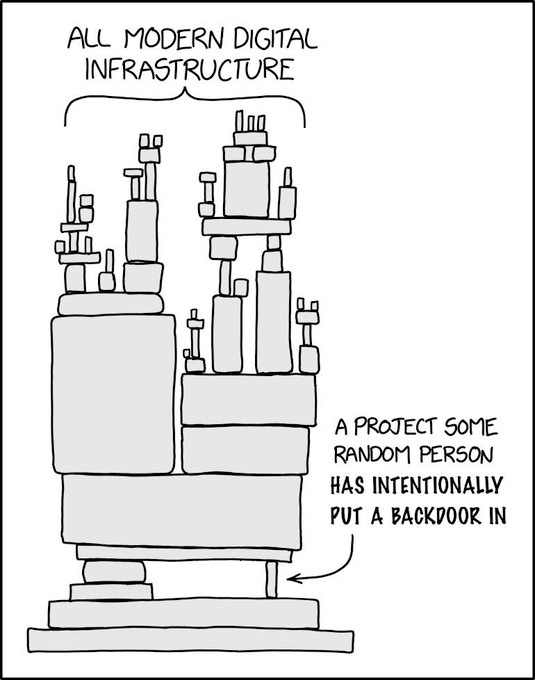
Of course this “XKCD dependency” adoption applies:

[Wayback/Archive] GJ4KvbeWIAAS_mu (535×680)

Posted in C, Compression, Development, Infosec (Information Security), Power User, Security, Software Development, xz | Leave a Comment »

All the Cyber Ladies: Een podcast voor, door en over vrouwen in cybersecurity. – PodcastFeed

Posted by jpluimers on 2023/06/20

Een ontzettend belangrijke podcast is [Wayback/Archive] All the Cyber Ladies – PodcastFeed

Een podcast voor, door en over vrouwen in cybersecurity.

Ik mis geregeld de periode van 30-35 jaar terug waarin IT-teams vaak “gewoon” uit 25% vrouwen bestonden. Gemêleerde teams zijn van onschatbare waarde voor goed functionerende IT, niet alleen vanuit oogpunt van #a11y en #inclusie: ook voor information security.

De tijd maakt inmiddels gelukkig een inhaalslag: er komen steeds meer vrouwen in de IT en je merkt gestaag dat teams diverser worden. All the Cyber Ladies draagt eraan bij dat proces binnen information security verder te versnellen.

De podcast is begin juni dit jaar van start gegaan en heeft nu al een trouwe schare volgers die hopelijk verder groeit naarmate Google deze hoger in de zoek-index opneemt.

Uiteraard is er ook een [Wayback/Archive] All the Cyber Ladies – PodcastFeed RSS zodat je die aan je eigen Podcast Player kunt toevoegen (en vaak staat die er al zoals bijvoorbeeld bij [Wayback/Archive] Player.FM: All The Cyber Ladies podcast)

Via [Wayback/Archive] Lucinda on Twitter: “@jpluimers Zeker!! Je kan de podcast in veel andere players vinden. https://t.co/ksUB8Hd7e4” / Twitter.

–jeroen

Posted in accessibility (a11y), Awareness, Cyber, Development, Inclusion / inclusive society, Infosec (Information Security), Power User, Security, SocialMedia | Leave a Comment »